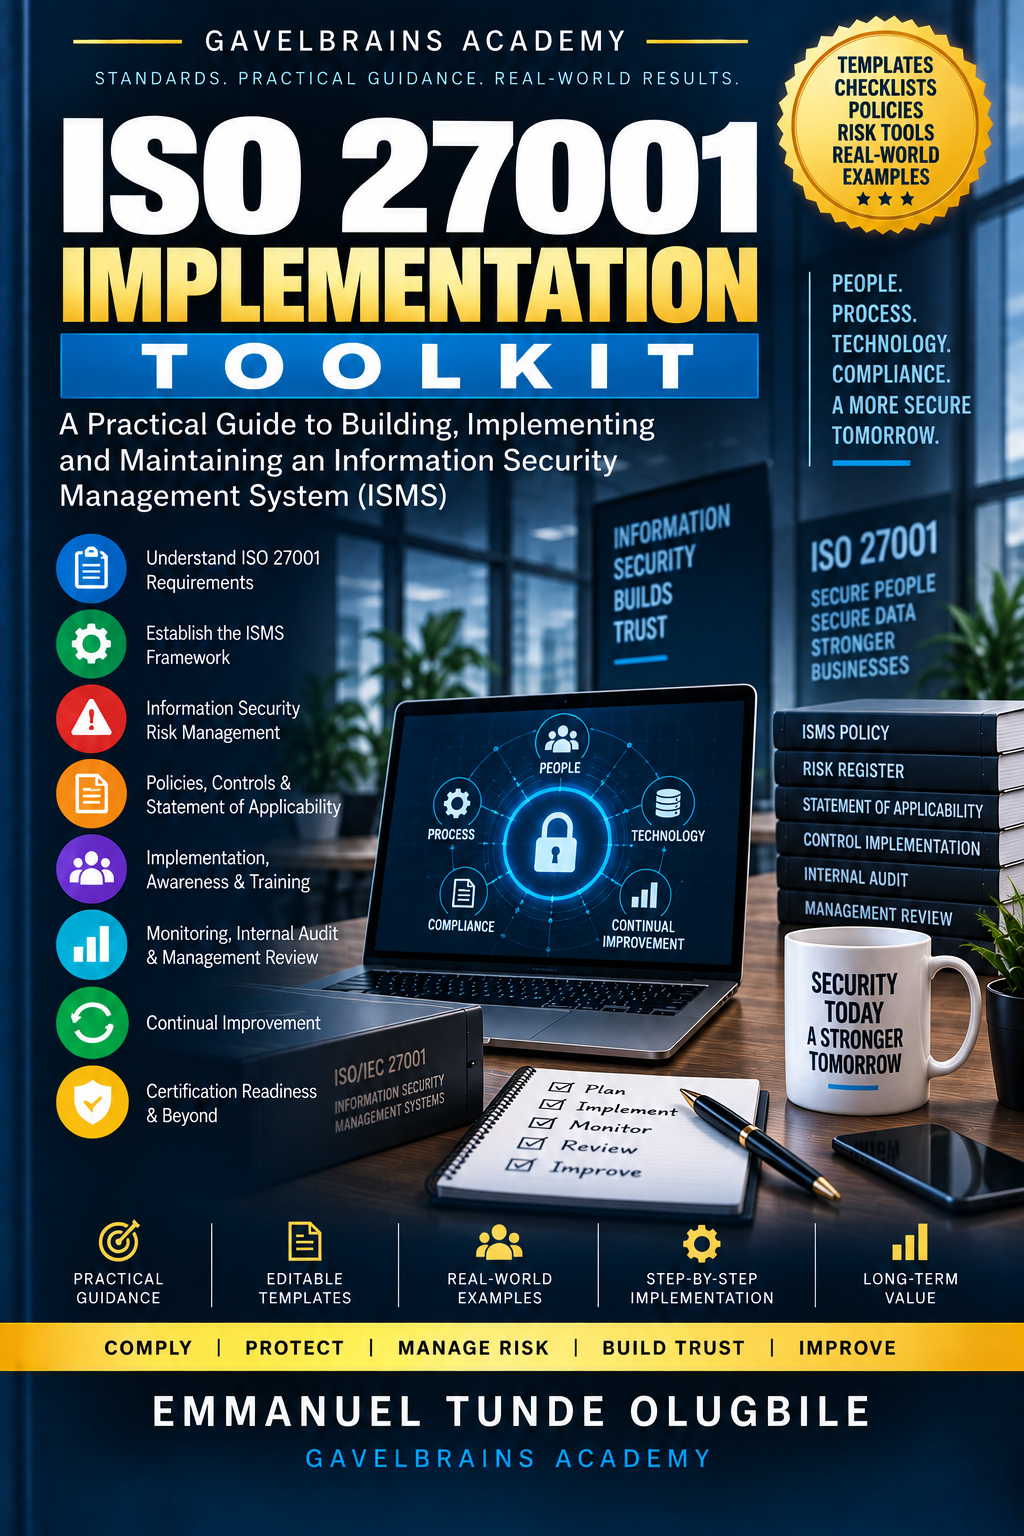
ISO 27001 Implementation Toolkit
Build a Structured Information Security Management System. Manage Risk. Strengthen Security Governance.
ISO 27001 Implementation Toolkit is a practical guide for cybersecurity, information security, GRC, risk, compliance, audit, and technology professionals seeking to understand and implement an Information Security Management System (ISMS) aligned with ISO/IEC 27001.
The book provides structured guidance across key implementation areas, including organizational context, ISMS scope, leadership, information security policies, risk assessment, risk treatment, the Statement of Applicability (SoA), security controls, documentation, performance monitoring, internal audits, management reviews, corrective actions, and continual improvement.
Readers learn how to translate ISO 27001 requirements into practical organizational activities—identifying information-security risks, selecting appropriate controls, assigning responsibilities, maintaining implementation evidence, preparing for internal reviews, tracking corrective actions, and improving the ISMS over time.
The toolkit also emphasizes the relationship between people, processes, technology, governance, risk, and evidence, helping readers understand that ISO 27001 implementation is not simply a documentation exercise but an ongoing management system for protecting information and managing security risk.
Designed for Information Security professionals, GRC practitioners, risk managers, IT managers, internal auditors, consultants, compliance teams, cybersecurity professionals, and organizations preparing for ISO 27001 implementation or certification, this toolkit provides a practical foundation for building a structured and sustainable ISMS.