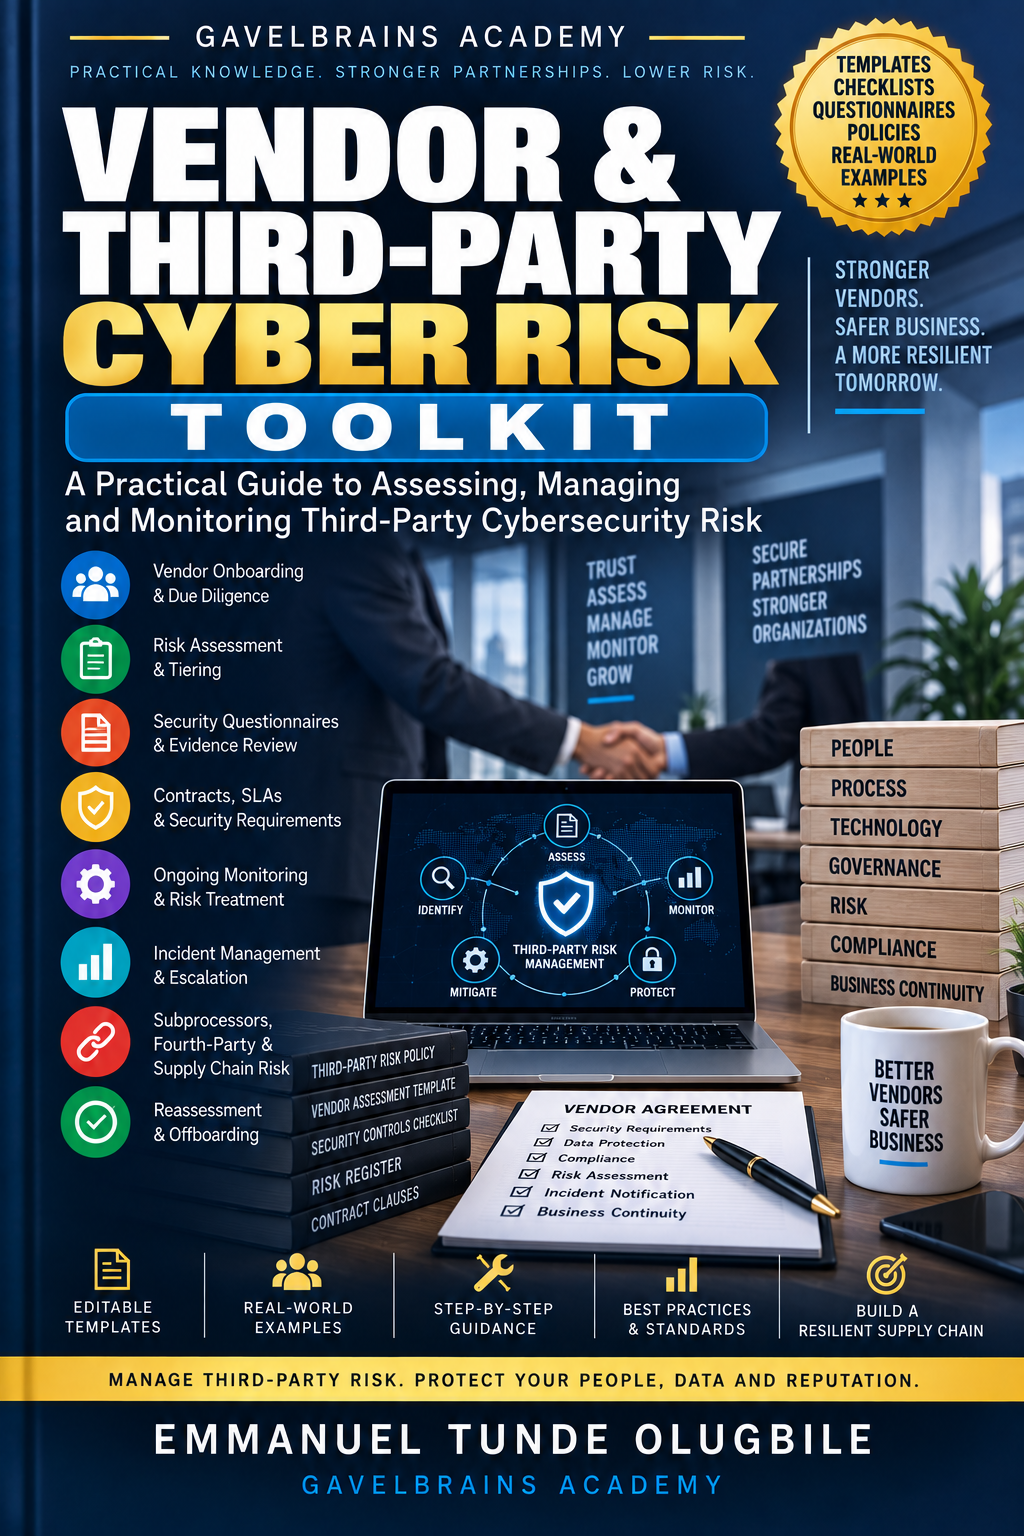
Vendor & Third-Party Cyber Risk Toolkit
Know Your Vendors. Assess the Risk. Protect Your Organization.
Vendor & Third-Party Cyber Risk Toolkit is a practical guide for cybersecurity, GRC, risk, procurement, compliance, and technology professionals responsible for managing the security risks introduced by vendors, suppliers, cloud providers, SaaS platforms, contractors, and other third parties.
The book provides a structured approach to the complete Third-Party Risk Management (TPRM) lifecycle, covering vendor inventory, criticality and risk tiering, due diligence, security questionnaires, evidence assessment, control evaluation, contractual security requirements, residual risk, remediation, continuous monitoring, reassessment, incident management, and secure vendor offboarding.
Readers learn how to evaluate important areas such as data access, identity and access management, encryption, security certifications, vulnerability management, incident response, business continuity, cloud security, privacy, subprocessors, fourth-party dependencies, and supply-chain risk.
The toolkit also helps professionals move beyond checklist-based vendor assessments by connecting evidence to business criticality, risk decisions, contractual safeguards, accountable ownership, and ongoing monitoring.
Designed for Third-Party Risk professionals, cybersecurity and GRC teams, risk managers, procurement professionals, IT leaders, consultants, auditors, and organizations, this book provides a practical foundation for building a more consistent and defensible vendor cyber-risk management program.